Topics

Explore critical topics shaping today’s SAP landscape—from digital transformation and cloud migration to cybersecurity and business intelligence. Each topic is curated to provide in-depth insights, best practices, and the latest trends that help SAP professionals lead with confidence.

Regions

Discover how SAP strategies and implementations vary across global markets. Our regional content brings localized insights, regulations, and case studies to help you navigate the unique demands of your geography.

Industries

Get industry-specific insights into how SAP is transforming sectors like manufacturing, retail, energy, and healthcare. From supply chain optimization to real-time analytics, discover what’s working in your vertical.

Hot Topics

Dive into the most talked-about themes shaping the SAP ecosystem right now. From cross-industry innovations to region-spanning initiatives, explore curated collections that spotlight what’s trending and driving transformation across the SAP community.

Topics

Explore critical topics shaping today’s SAP landscape—from digital transformation and cloud migration to cybersecurity and business intelligence. Each topic is curated to provide in-depth insights, best practices, and the latest trends that help SAP professionals lead with confidence.

Regions

Discover how SAP strategies and implementations vary across global markets. Our regional content brings localized insights, regulations, and case studies to help you navigate the unique demands of your geography.

Hot Topics

Dive into the most talked-about themes shaping the SAP ecosystem right now. From cross-industry innovations to region-spanning initiatives, explore curated collections that spotlight what’s trending and driving transformation across the SAP community.
SOX compliance

Access Governance: The Critical Path Through Your S/4HANA Transformation JourneyPathlock
Modern Identity Management for SOX: Closing Control Gaps Across SAPSolving the SoD and user administration challenge for human and agentic actors As SOX compliance expectations continued to rise, many organizations still lacked complete visibility and control over who—and what—had access to critical SAP and SOX-relevant enterprise applications. The root issue was structural. Enterprise IAM was designed to manage identity at scale, but SOX required access governance to operate as a financial control system aligned with financial reporting risk and audit defensibility. In modern landscapes where financial processes ran across multiple systems, access could appear compliant within individual applications while still introducing material risk across the end-to-end workflow. KPMG’s most recent material weakness study underscored the point: among companies disclosing material weaknesses, 56% cited IT, software, security, and access issues—and 43% cited segregation of duties or control design weaknesses. These control gaps drove a rising cost of compliance. The 2025 KPMG SOX Survey reported an FY24 average program effort of 15,580 hours, with 45% of organizations reporting year-over-year cost increases. When access governance was weak by design, teams compensated with manual controls, spreadsheet-driven reviews, late-cycle remediation, and repeated audit retesting—creating friction across Finance, IT, IAM, and Internal Audit. This session addressed the identity and access breakdowns that repeatedly surfaced in audits: disconnected joiner-mover-leaver processes that created access creep, SoD conflicts that didn’t map cleanly to financial workflows across applications, privileged access that wasn’t governed as a repeatable, auditable control, and high-volume user access reviews that generated evidence but limited assurance. The speakers also addressed a fast-growing blind spot: the lifecycle and governance of non-human identities—including service accounts, bots, and automation agents—that interacted with SOX systems without consistent ownership or enforceable boundaries. The session included a demonstration of how identity discovery, access governance, and continuous compliance monitoring could be automated across SAP and adjacent applications using a modern identity security platform
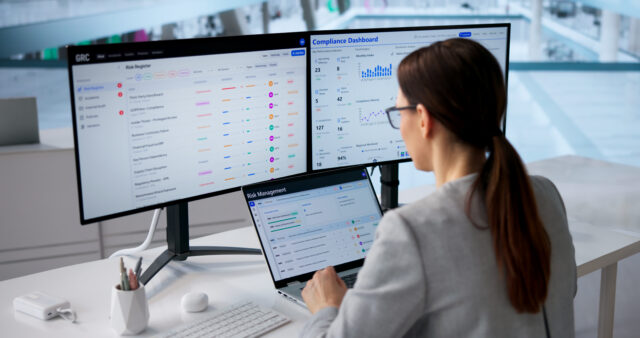
Streamlining SAP User Access Review (UAR): Common PainYour SAP User Access Review process might be checking a compliance box — while quietly creating a bigger risk. Between reviewers who ghost their approval requests, leadership refusing to touch GRC escalations, and role owners left validating access for employees who've already exited the organization, UAR execution is riddled with breakdowns that most organizations don't surface until an audit forces the question. With SOX, GDPR, and ISO 27001 all demanding rigorous access oversight, a bottlenecked or poorly scoped review cycle isn't just an inconvenience — it's exposure. So where exactly do most SAP UAR programs fall apart, and what does a smarter, automated approach actually look like? Here's the full breakdown.
security
The Silent Killers of SAP Security: How to Shut Down Dormant and Unmitigated Access RisksSAP Governance, Risk, and Compliance (GRC) has evolved from a periodic compliance task to a risk-based approach, exemplified by ToggleNow's ReviewNow solution, which automates around 99% of User Access Reviews using real-time SAP data, enabling deeper insights into access governance.

Events

07Dec
SAPinsider Technology Executive ForumPhoenix, Arizona, United States
15Mar
SAPinsider Las Vegas 2027Las Vegas, Nevada, NV
View All

Related Vendors