Explore critical topics shaping today’s SAP landscape—from digital transformation and cloud migration to cybersecurity and business intelligence. Each topic is curated to provide in-depth insights, best practices, and the latest trends that help SAP professionals lead with confidence.
Discover how SAP strategies and implementations vary across global markets. Our regional content brings localized insights, regulations, and case studies to help you navigate the unique demands of your geography.
Get industry-specific insights into how SAP is transforming sectors like manufacturing, retail, energy, and healthcare. From supply chain optimization to real-time analytics, discover what’s working in your vertical.
Dive into the most talked-about themes shaping the SAP ecosystem right now. From cross-industry innovations to region-spanning initiatives, explore curated collections that spotlight what’s trending and driving transformation across the SAP community.
Explore critical topics shaping today’s SAP landscape—from digital transformation and cloud migration to cybersecurity and business intelligence. Each topic is curated to provide in-depth insights, best practices, and the latest trends that help SAP professionals lead with confidence.
Discover how SAP strategies and implementations vary across global markets. Our regional content brings localized insights, regulations, and case studies to help you navigate the unique demands of your geography.
Get industry-specific insights into how SAP is transforming sectors like manufacturing, retail, energy, and healthcare. From supply chain optimization to real-time analytics, discover what’s working in your vertical.
Dive into the most talked-about themes shaping the SAP ecosystem right now. From cross-industry innovations to region-spanning initiatives, explore curated collections that spotlight what’s trending and driving transformation across the SAP community.
A critical vulnerability (CVE-2025-55182) affecting React Server Components, scored CVSSv3 10.0, allows Remote Code Execution due to an insecure deserialization logic error in the ReactFlight protocol.
Affected versions of React components include 19.0, 19.1.0, 19.1.1, and 19.2.0, with Next.js users urged to upgrade to specific safe versions (15.0.5 or later).
Immediate patching is recommended as no proof-of-concept exploit exists; other frameworks relying on React Server Components may also be impacted.
A critical vulnerability affecting React Server Components has been announced, allowing Remote Code Execution via insecure deserialization in affected versions, urging users to update their software immediately.
A critical vulnerability was announced today affecting React Server Components (RSC), which affects React (CVE-2025-55182) and all frameworks using RSC, notably Next.js (CVE-2025-66478).
Both vulnerabilities were given a CVSSv3 10.0 score, marking them as highly critical.
The source of these vulnerabilities was found in RSC’s ReactFlight protocol – a protocol used by React 19 to serialize and deserialize data between the server and the client. An insecure deserialization logic error was found, which allows specially-crafted HTTP requests to trigger Remote Code Execution on the receiving server.
Vulnerable React components include versions 19.0, 19.1.0, 19.1.1, and 19.2.0 of react-server-dom-parcel, react-server-dom-webpack, and react-server-dom-turbopack
These vulnerable components are included in Next.js using App Router with versions ≥14.3.0-canary.77, ≥15 and ≥16.
Other frameworks utilizing the above mentioned React components or depend on RSC may also be vulnerable.
A proof-of-concept exploit for these vulnerabilities is not available as of writing this, but due to the high severity and impact of these vulnerabilities, it is recommended to patch immediately.
Users of React are urged to update to versions 19.0.1, 19.1.2, or 19.2.1.
Next.js users should upgrade to versions 15.0.5, 15.1.9, 15.2.6, 15.3.6, 15.4.8, 15.5.7, or 16.0.7.
How can Orca help?
The Orca Cloud Security Platform continuously scans for vulnerabilities in your cloud environments, including AWS, Azure, Google, Kubernetes, and others. When Orca finds a vulnerability, it will immediately create an alert and assign a risk score by considering the full contextual picture of the risk and the surrounding cloud environment so teams know which vulnerabilities need to be patched first.
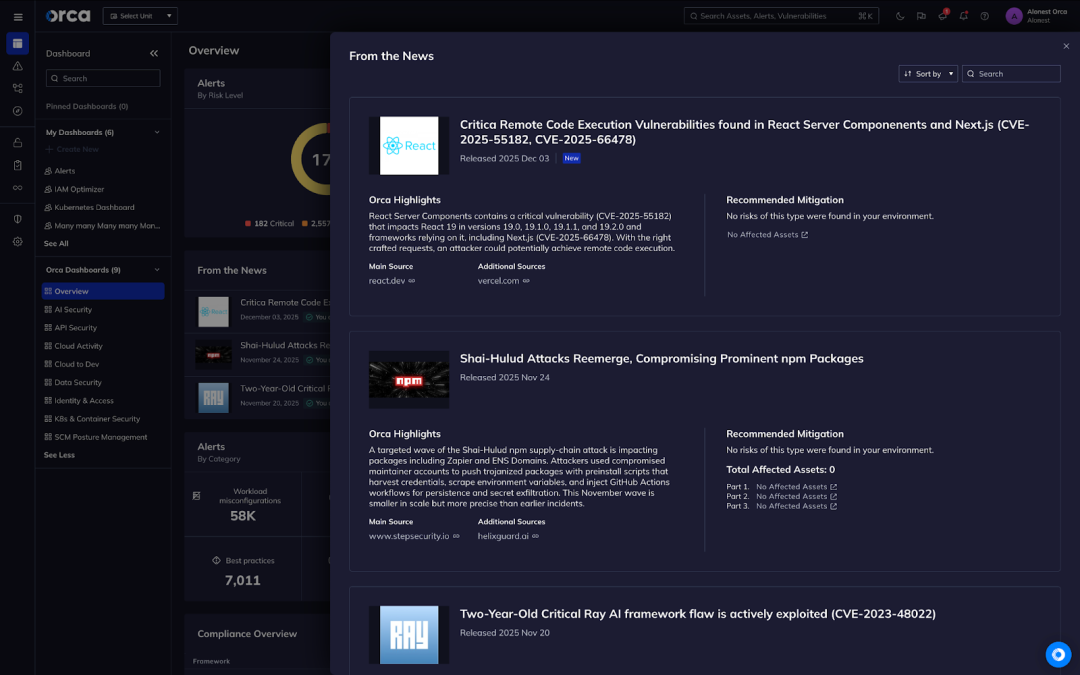
The Orca Platform displays trending vulnerabilities in the “From the News” widget of the Orca dashboard. Users can see if their environment is vulnerable to the vulnerabilities and how to remediate them.