Explore critical topics shaping today’s SAP landscape—from digital transformation and cloud migration to cybersecurity and business intelligence. Each topic is curated to provide in-depth insights, best practices, and the latest trends that help SAP professionals lead with confidence.
Discover how SAP strategies and implementations vary across global markets. Our regional content brings localized insights, regulations, and case studies to help you navigate the unique demands of your geography.
Get industry-specific insights into how SAP is transforming sectors like manufacturing, retail, energy, and healthcare. From supply chain optimization to real-time analytics, discover what’s working in your vertical.
Dive into the most talked-about themes shaping the SAP ecosystem right now. From cross-industry innovations to region-spanning initiatives, explore curated collections that spotlight what’s trending and driving transformation across the SAP community.
The release of the SAPMAP toolkit, an open-source exploitation resource, highlights a significant risk for SAP customers due to its inclusion of PoC exploits for critical vulnerabilities previously patched by SAP.
This change is crucial because it enables attackers to launch automated attacks against unprotected SAP systems, potentially leading to data breaches, operational disruptions, and ransomware deployment, impacting businesses heavily reliant on SAP environments.
Both SAP customers and IT security teams must take immediate action to patch their systems and monitor for exploitation attempts, as the SAPMAP toolkit could empower threat actors to exploit vulnerabilities quickly and effectively.
On September 15th, researchers released SAPMAP, an open-source toolkit for exploiting SAP vulnerabilities, which includes multiple exploits and a ransomware PoC, prompting urgent security recommendations for SAP users to assess risks and apply patches against potential attacks.
On September 15th, a group of researchers publicly released an open-source SAP discovery and exploitation toolkit (dubbed “SAPMAP”). This toolkit contains multiple exploits for various known SAP vulnerabilities and offensive security capabilities for targeting SAP systems, also including proof-of-concept (PoC) exploits for critical SAP vulnerabilities patched by SAP earlier this month.
This article analyzes the offensive security capabilities released, and provides SAP customers with recommendations on how to assess business risk and mitigation strategies against potential unauthorized use of this new toolkit.
We will continue to monitor our Global SAP Threat Intel Network for various types of attack activity, and deliver updates to the SAP community as well as further in-product support and communication to our Onapsis customers.
SAPMAP is an SAP exploitation toolkit that bears some similarities to BloodHound (for Microsoft Active Directory and EntraID) and Metasploit. While originally gated, the open-source toolkit was introduced into the public domain on GitHub, licensed under GPL 3.0. Within the SAPMAP toolkit, users have access to several SAP exploits, ransomware PoCs, discovery and automation tooling, and other very powerful offensive security capabilities. The toolkit also includes an exploit for CVE-2025-31324, which was the single most frequently-exploited vulnerability in the world last year according to the Mandiant M-Trends 2026 report. The collective capabilities in this toolkit enable operators to perform automated attacks against SAP landscapes, resulting in the full compromise of unprotected SAP business-critical systems, data and processes.
In terms of capabilities, SAPMAP can automatically map an organization’s entire SAP environment, spanning both on-premises systems and cloud (including SAP BTP). Further, it offers PoCs for lateral movement and local privilege escalation (e.g., over RFC). It traverses trust boundaries in both directions to plot attack paths from an initial foothold all the way to full system control. It even offers an SAP ransomware deployment PoC, visualizations, and a one-click automation that chains every offensive capability that SAPMAP has into a self-driving, converging loop (i.e., SCAN->EXPLOIT->ENRICH->PROPAGATE).
Onapsis Research Labs performed an initial analysis of the contents of SAPMAP, in particular, the “exploitation” folder. At the time of publishing, the contents of that folder contain modules in the following categories.
Core Offensive Capabilities and Exploit Modules
Category
Number of Files
Description
Standalone Pre-Authentication Exploits
10 files
These exploits require no target credentials. Any attacker with network access to the relevant SAP ports can execute attacks remotely.
Post-Authentication Activity
8 files
Actions designed for execution on already compromised SAP systems
Windows / Local Privilege Escalation (LPE) & AV-Evasion
10 files
Tools targeting LPE, security bypass, etc.
Library / Helpers
6 files
Supporting utility code
Orchestrators
2 files
Framework management tools
Of these, the most critical category is the Standalone Pre-Authentication Exploits category, as the contents include exploits that do not require an account in the target SAP system.
At the same time, the Post-Authentication Activity folder provides significant offensive capabilities that a toolkit user could leverage on a compromised SAP system. Of considerable note are the following three:
SAP Ransomware PoC Tool – Capability to perform basic encryption of SAP business information and send ransomware notes to SAP users, including a “pre-configured list of high-impact tables” for the operator to target and encrypt the most critical business data tables in a target SAP system.
Direct Database Injection – SAP user creation through SQL injection directly into USR02/UST04/USRBF2 tables via operating system command line interfaces (CLI) through SAPXPG, bypassing identity, GRC and segregation of duties controls.
SAP TMS Propagation – Uses wormlike functionality to auto-propagate a malicious SAP transport object across all SAP systems.
SAP Business Risk and Impact Analysis
The SAPMAP toolkit delivers a complete and comprehensive set of SAP offensive capabilities, including weaponized exploits for some of the most critical, preauthentication SAP vulnerabilities in recent memory – including PoC exploits for critical vulnerabilities patched by SAP earlier this month. Successful exploitation can result in full compromise of unprotected SAP systems business-critical data and processes. This can include exfiltration, tampering and/or deletion of critical SAP-hosted business data, disruption of mission-critical SAP business processes, deployment of ransomware in SAP, lateral movement, and more.
The toolkit ships with an integrated MCP server, including more than 30 tools and resources, so the entire attack functionality including AutoPwn (the scan→exploit→propagate convergence loop) and RanSAPware (the ransomware module) is wired up as tools that LLM agents can invoke directly over MCP. In other words, the toolkit is explicitly designed for autonomous, AI-driven operation of the full SAP exploitation chain, not just manual GUI use.
A Note on PoCs/Exploits for New Critical Vulnerabilities OVERPASS and S4GET
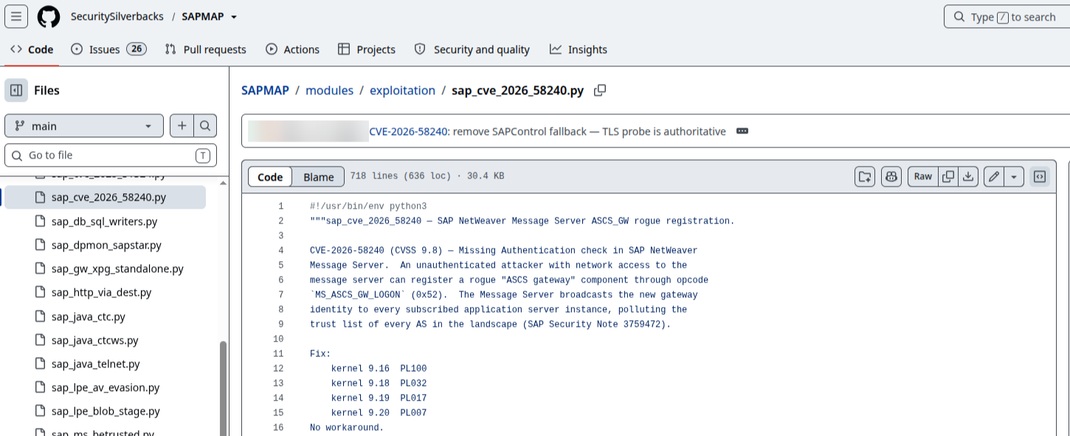
In addition to several vulnerabilities SAP has patched long time ago, SAPMAP also contains exploits/PoCs for two vulnerabilities only recently patched by SAP on September 8th: S4GET (CVE-2026-58240) and OVERPASS (CVE-2026-44756). These zero-day vulnerabilities were originally discovered by the Onapsis Research Labs, who worked in close collaboration with SAP to mitigate them (for more information see the on-demand SAP+Onapsis threat briefing).
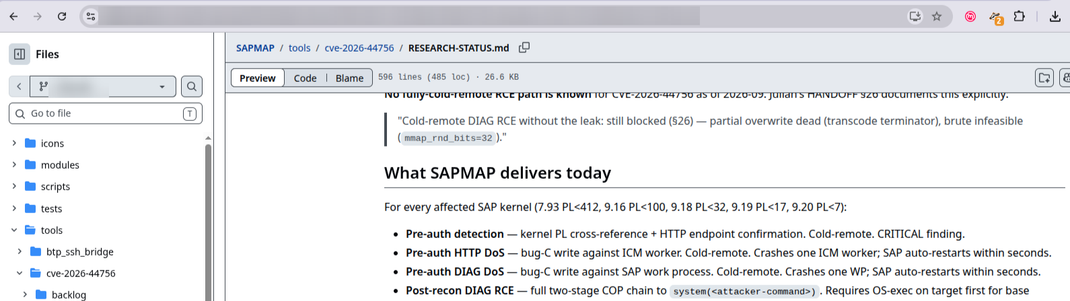
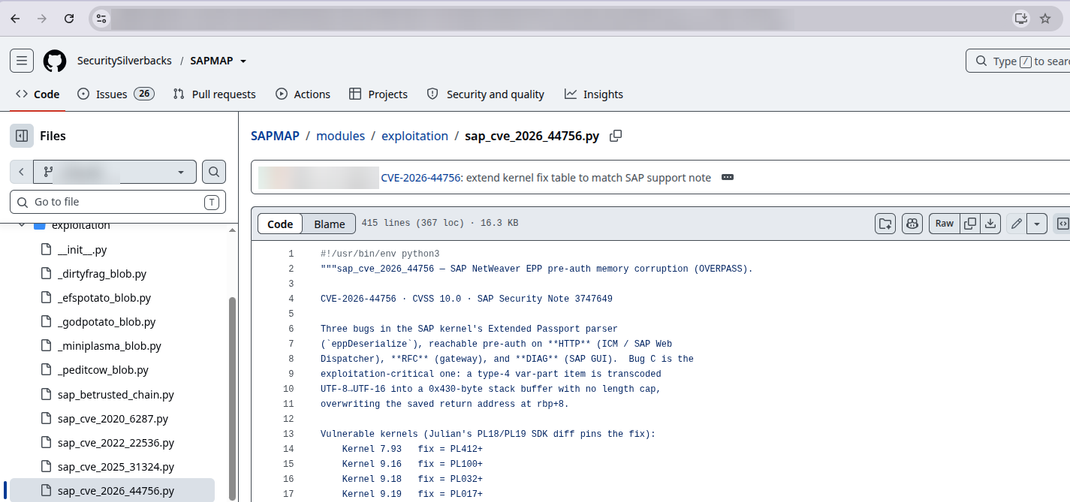
In the case of OVERPASS, while the maintainers initially indicated that related exploits were being withheld from public release, the Onapsis Research Labs detected that they were in fact included in the repository commits.
Onapsis Research Labs has reported this to the project maintainers. It’s worth noting that all clones of the repository since its original publication include these previously-committed files. Defenders should operate under the assumption that OVERPASS exploit PoCs have been made publicly available.
Recommended Actions for SAP Exposure Management
Onapsis Research Labs strongly advises all SAP customers to ensure their landscapes are fully patched with the relevant SAP Security Notes, prioritizing protection against OVERPASS, S4GET and the Standalone Pre-Authentication Exploitations contained within this toolkit:
In general, a good order of operations for comprehensive SAP exposure management and patching of systems is as follows:
Assess and identify vulnerable SAP applications in your environment (don’t forget shadow and non-production systems.)
Apply the relevant SAP Security Notes. Prioritize applying notes to SAP systems exposed to the internet, then work inwards. Consider that internal systems still represent a large attack surface as affected components are commonly accessible even through internal firewalls in corporate networks.
Reduce attack surface and reachability where your architecture allows.
Monitor for exploitation attempts. Ensure you have visibility into your SAP application layer, so that attempts to exploit these vulnerabilities can be detected.
Defending SAP Landscapes with the Onapsis Platform
Over the years, Onapsis Research Labs have had a long history of partnering with SAP to mitigate many of the most critical vulnerabilities to affect SAP systems. In our deeper analysis of the SAPMAP toolkit, we learned that the Onapsis security researchers responsibly reported and helped SAP mitigate 7 of the 10 featured vulnerabilities. This means that Onapsis Defend customers have already received proactive SAP zero-day protection for most of these issues, in cases even months before the SAP Security Notes became available.
It’s imperative for enterprises to leverage focused SAP cybersecurity automation capabilities, rooted in high-fidelity threat intelligence, such as those found in the Onapsis Platform. Exposure management from Onapsis Assess and continuous threat and exploit monitoring from Onapsis Defend are underwritten by insights from the Onapsis Research Labs and the telemetry from our Global SAP Threat Intel Network. Collectively, these capabilities deliver significant protection from threat actors armed with both private and public exploits or toolkits.
Immediate Protection Steps for Onapsis Customers
Onapsis Research Labs strongly advises all Onapsis customers to take the following immediate steps in the Onapsis Platform:
Expedite Vulnerability Scanning & Patching with Onapsis Assess: Immediately audit all SAP assets using Onapsis Assess and prioritize patching any systems vulnerable to the exploits packaged in SAPMAP.
Activate Real-Time Threat Monitoring with Onapsis Defend: Continuously monitor SAP environments for indicators of compromise, unauthorized administrative activity, or exploitation attempts. Onapsis Research Labs discovered and helped mitigate most of these vulnerabilities, which means Defend has multiple rules in place to protect against potential exploitation, even during the time patches are in the process of being rolled out.
Conclusion: Securing Your Enterprise Against SAPMAP
SAPMAP pairs PoC exploits for some very critical SAP vulnerabilities with significant offensive capabilities. As with any powerful toolkit that becomes broadly available, the priority for SAP customers is straightforward: make sure your landscape is protected, patch the underlying vulnerabilities and ensure you have visibility to detect exploitation attempts. The Onapsis Research Labs will continue to monitor the threat landscape and support the SAP community accordingly.